API Security Basics for Sysadmins (Ops View)
What ops must know about APIs: TLS, authn/z, secrets, rate limits, inventory — defensive and high-level.

Server hardening, API security, CVEs, threat defence and legal bug bounty practice for sysadmins
What ops must know about APIs: TLS, authn/z, secrets, rate limits, inventory — defensive and high-level.
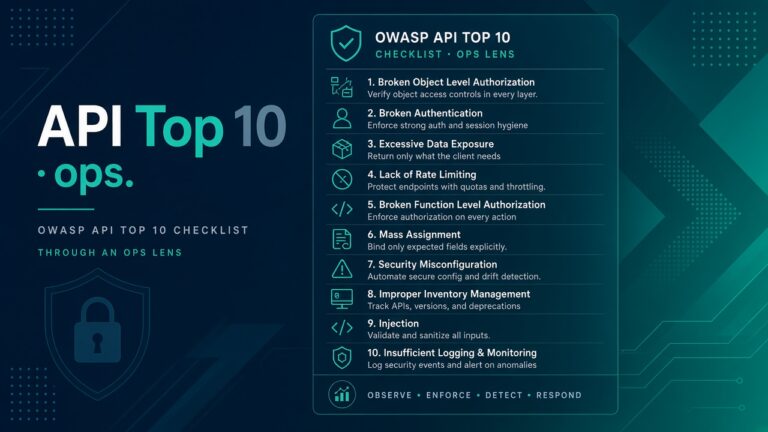
High-level OWASP API Top 10 for operators: exposure, auth misconfig, inventory, and monitoring — no attack steps.
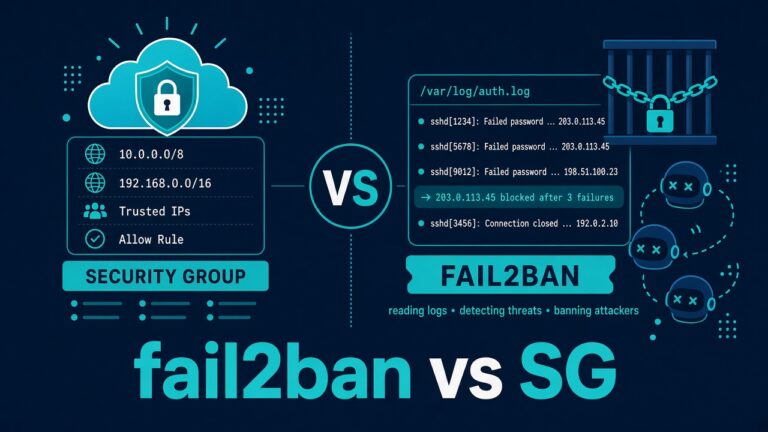
fail2ban bans bad actors in logs; cloud security groups block ports at the edge. Use both on purpose — here’s what each actually stops.
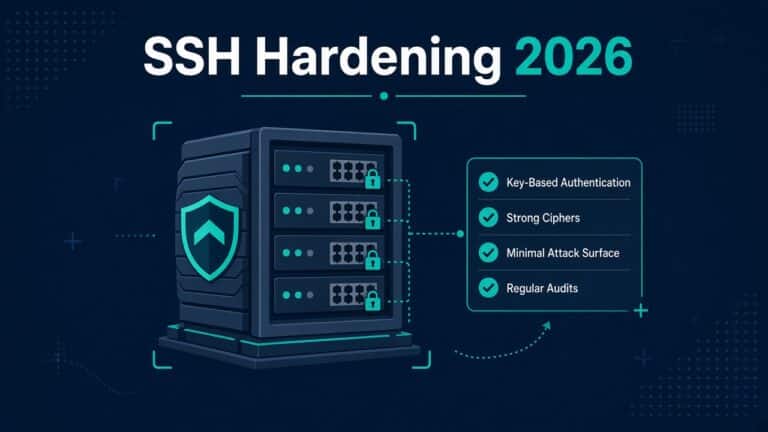
Actionable 2026 SSH hardening checklist: keys only, PermitRootLogin, fail2ban, MFA basics, and config snippets that survive real ops.
What NTFS alternate data streams are, how to create, list and delete them with cmd and PowerShell, and why attackers and defenders care.

Five practical habits that stop most Windows infections: patching, unique passwords with MFA, phishing awareness, Defender and the firewall, and tested backups.