API Security Basics for Sysadmins (Ops View)
What ops must know about APIs: TLS, authn/z, secrets, rate limits, inventory — defensive and high-level.
What ops must know about APIs: TLS, authn/z, secrets, rate limits, inventory — defensive and high-level.
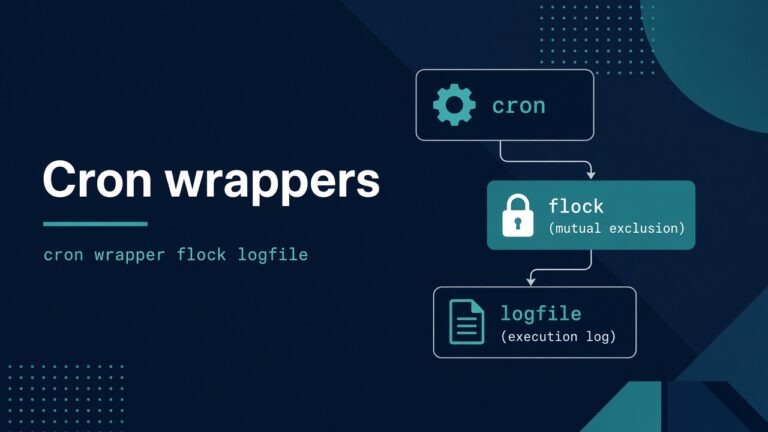
Wrap Bash scripts for cron with locks, PATH, logs, timeouts, and exit codes — so night jobs stay boring.
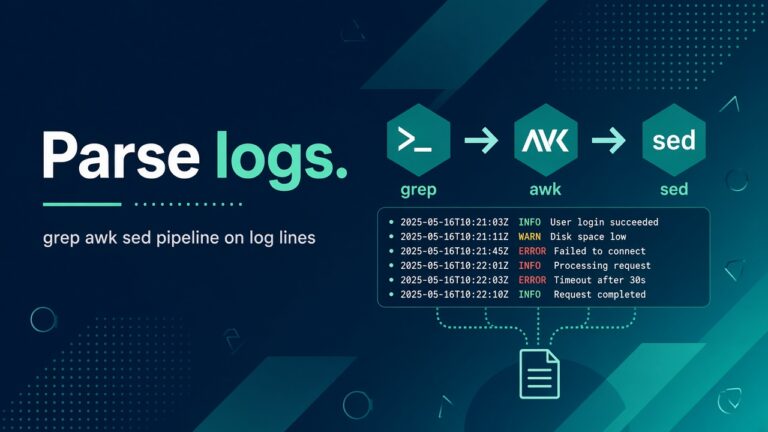
Practical grep, awk, and sed for sysadmins on real log shapes — nginx, auth, journal — without one-liner worship.
set -euo pipefail, traps, and logs that help at 2 AM — practical Bash error handling for sysadmins.
Practical Bash for ops automation: readable scripts, safe defaults, exit codes, and habits that survive 2 AM — not CTF cleverness.
Practice sysadmin interview scenarios with structured answers: disk full, SSH fail, bad unit, DNS, load — how hiring managers listen.
Day-1 Linux networking for ops: interfaces, routes, DNS, ss, curl, and a triage order that works under pressure.
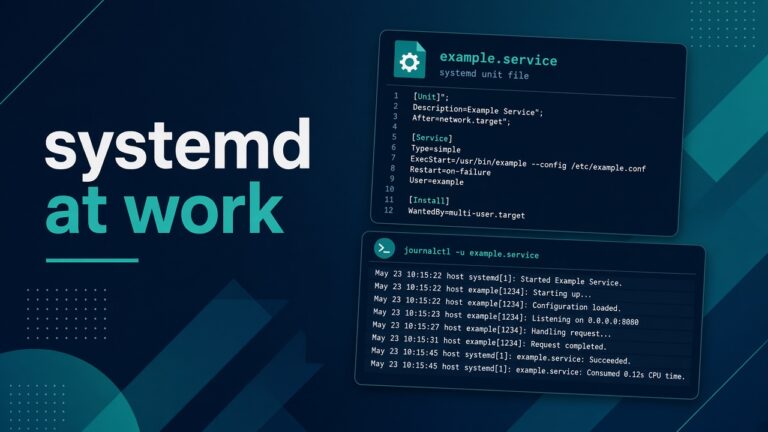
systemd units, journals, restarts, and timers the way junior admins meet them on the job — practical, not encyclopedia.
Use apt and dnf like production ops: updates, holds, repos, cleanup, and “what changed?” — not student homework installs.
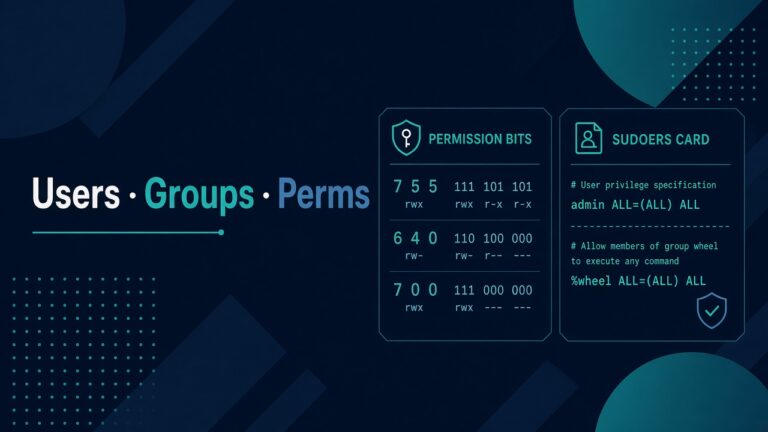
Users, groups, sudo, and permissions the way ops uses them at work — less theory fog, more “why can’t this service write here?”